Install KubeRocketCI
To install KubeRocketCI, deploy the prerequisites (Tekton, cert-manager, and the NGINX Ingress Controller) and then install the platform itself with Helm on any Kubernetes cluster. This quick start walks through these steps and ends with your first login to the KubeRocketCI Portal — no prior platform experience required.
Install Tekton
KubeRocketCI relies on Tekton resources, including Tasks, Pipelines, Triggers, and Interceptors to execute CI/CD pipelines.
To install Tekton, run the commands below:
kubectl apply -f https://infra.tekton.dev/tekton-releases/pipeline/previous/v1.6.2/release.yaml
kubectl apply -f https://infra.tekton.dev/tekton-releases/triggers/previous/v0.36.0/release.yaml
kubectl apply -f https://infra.tekton.dev/tekton-releases/triggers/previous/v0.36.0/interceptors.yaml
Install cert-manager
The KubeRocketCI operators rely on cert-manager to issue the TLS certificates for their admission webhooks.
To install cert-manager, run the command below:
kubectl apply -f https://github.com/cert-manager/cert-manager/releases/download/v1.21.2/cert-manager.yaml
Install NGINX Ingress Controller
The KubeRocketCI Portal sends its session cookie over HTTPS only. The NGINX Ingress Controller provides the HTTPS endpoint for opening the Portal.
To install the NGINX Ingress Controller, run the command below:
kubectl apply -f https://raw.githubusercontent.com/kubernetes/ingress-nginx/controller-v1.15.1/deploy/static/provider/cloud/deploy.yaml
Install platform
To deploy the platform, follow the steps below:
-
Wait until the prerequisites are ready:
kubectl wait deployment --all --for=condition=Available --timeout=300s -n tekton-pipelineskubectl wait deployment --all --for=condition=Available --timeout=300s -n cert-managerkubectl wait pod --selector=app.kubernetes.io/component=controller --for=condition=Ready --timeout=300s -n ingress-nginx -
Add a Helm Chart repository:
helm repo add epamedp https://epam.github.io/edp-helm-charts/stablehelm repo update -
Create the
krcinamespace and theportal-secretsecret. The Portal uses theSERVER_SECRETkey of this secret to protect user sessions:kubectl create namespace krcikubectl create secret generic portal-secret -n krci --from-literal=SERVER_SECRET="$(openssl rand -base64 32)" -
Create the
values.yamlfile with the following content:values.yamlglobal:# Wildcard DNS name that resolves to the local machinednsWildCard: 127.0.0.1.nip.iokrci-portal:ingress:className: nginx# The Portal host is krci-portal-<namespace>.<dnsWildcard>: krci-portal-krci.127.0.0.1.nip.iodnsWildcard: 127.0.0.1.nip.io# The Portal reads its configuration from the portal-secret Secret# and from the portal-config ConfigMap, which the chart renders from configEnvextraEnvFrom:- secretRef:name: portal-secret- configMapRef:name: portal-configconfigEnv:# No identity provider is used in this guide,# so the Portal offers only the service account token loginOIDC_ISSUER_URL: "" -
Deploy the platform using the
helm installcommand:helm install krci epamedp/edp-install --version 3.15.0 --wait -n krci --values values.yaml -
Upon successful deployment of the KubeRocketCI Helm Chart, run the
kubectl port-forwardcommand to reach the ingress controller:kubectl port-forward service/ingress-nginx-controller 8443:443 -n ingress-nginx -
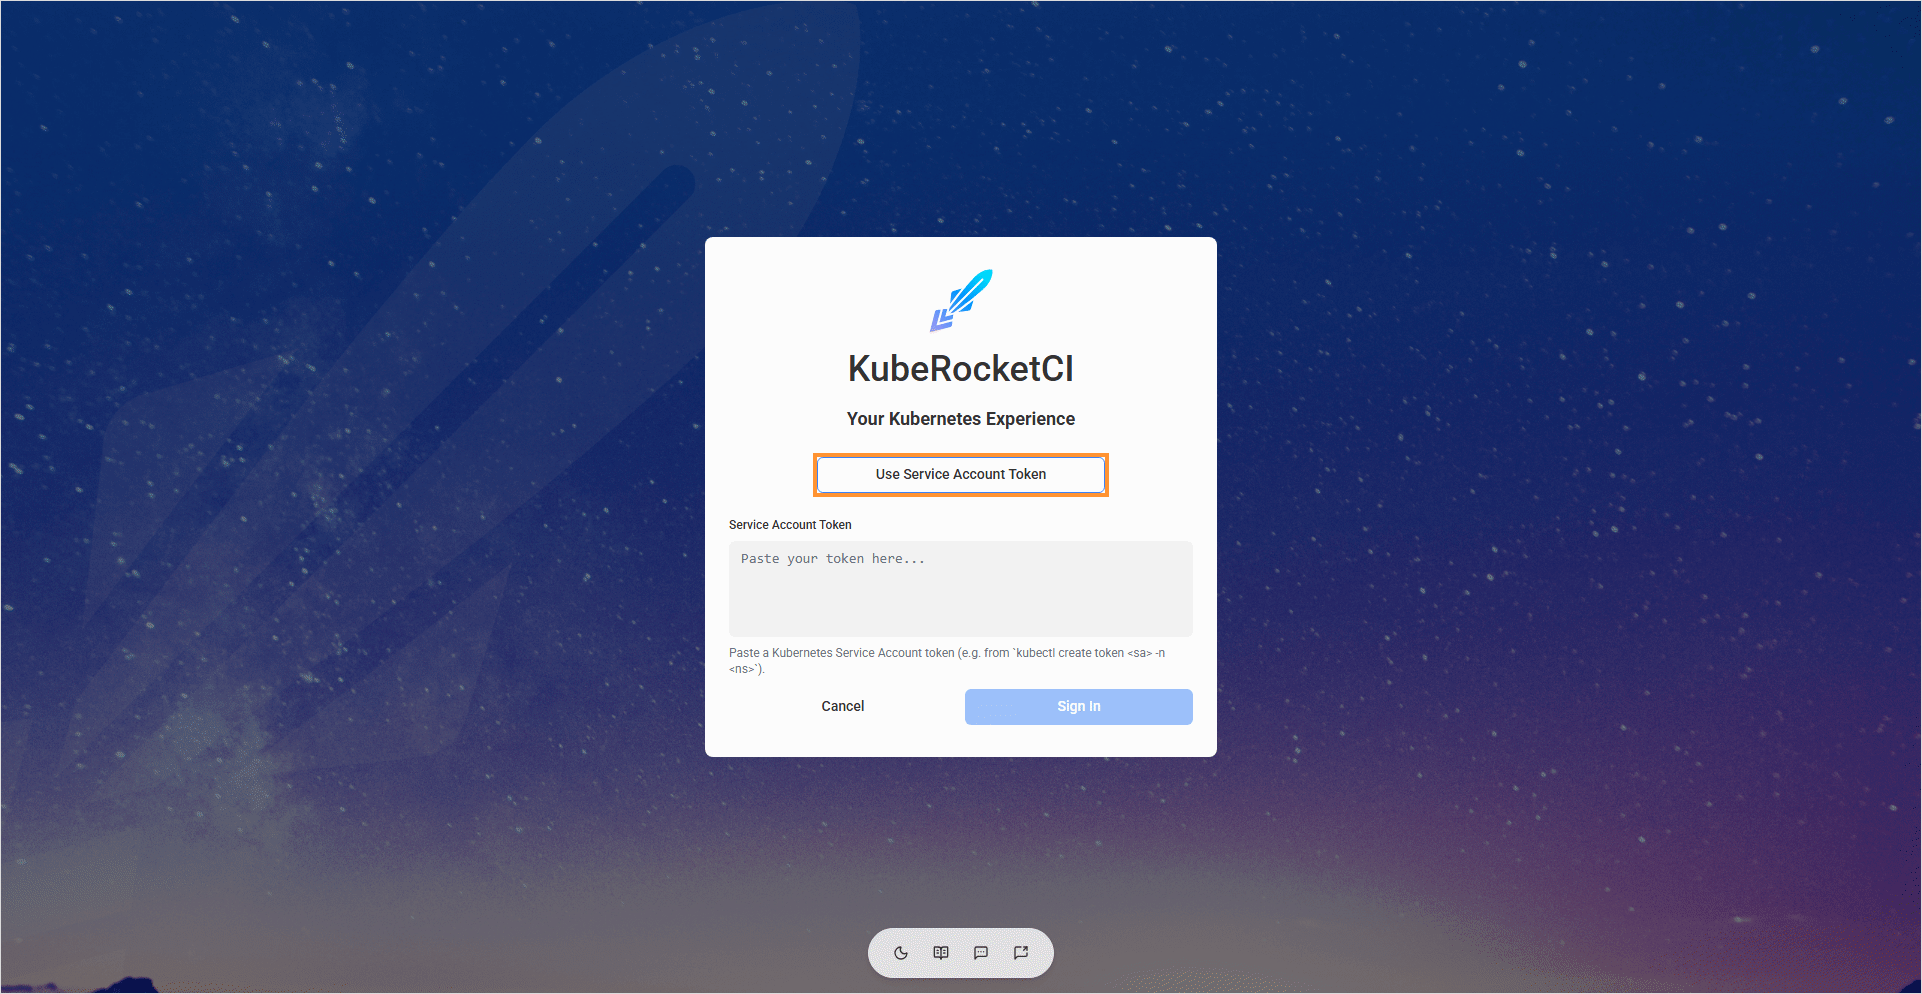
Open the Portal in your browser to access the login menu and click Use Service Account Token:
https://krci-portal-krci.127.0.0.1.nip.io:8443noteThe ingress controller serves a self-signed certificate, so the browser shows a security warning. Accept it to proceed to the Portal.
-
Create the edp-admin service account and generate its token to open the KubeRocketCI:
kubectl -n krci create serviceaccount edp-adminkubectl create clusterrolebinding edp-admin --serviceaccount=krci:edp-admin --clusterrole=cluster-adminkubectl create token edp-admin -n krci -
In the login menu, paste the generated token in the Service Account Token field and click the Sign In button.
-
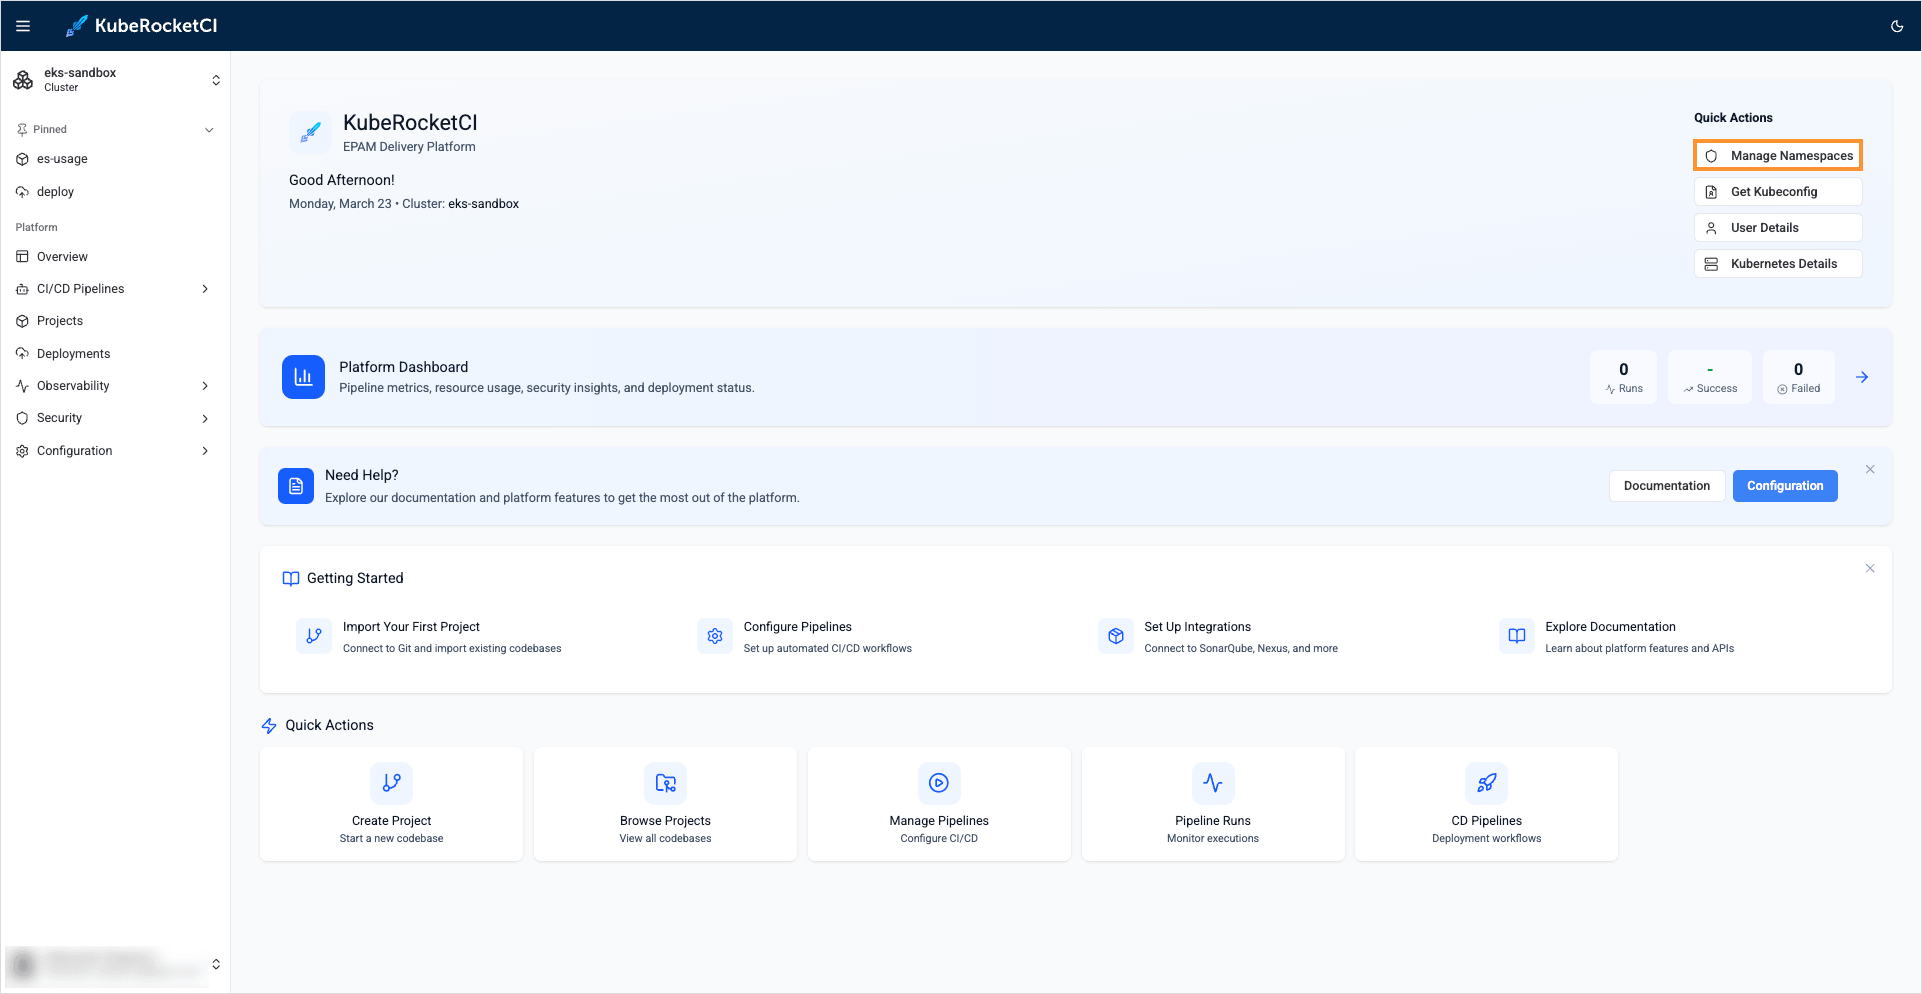
Upon logging in, open the namespaces window by clicking the Manage Namespaces button in the top right corner of the page:
-
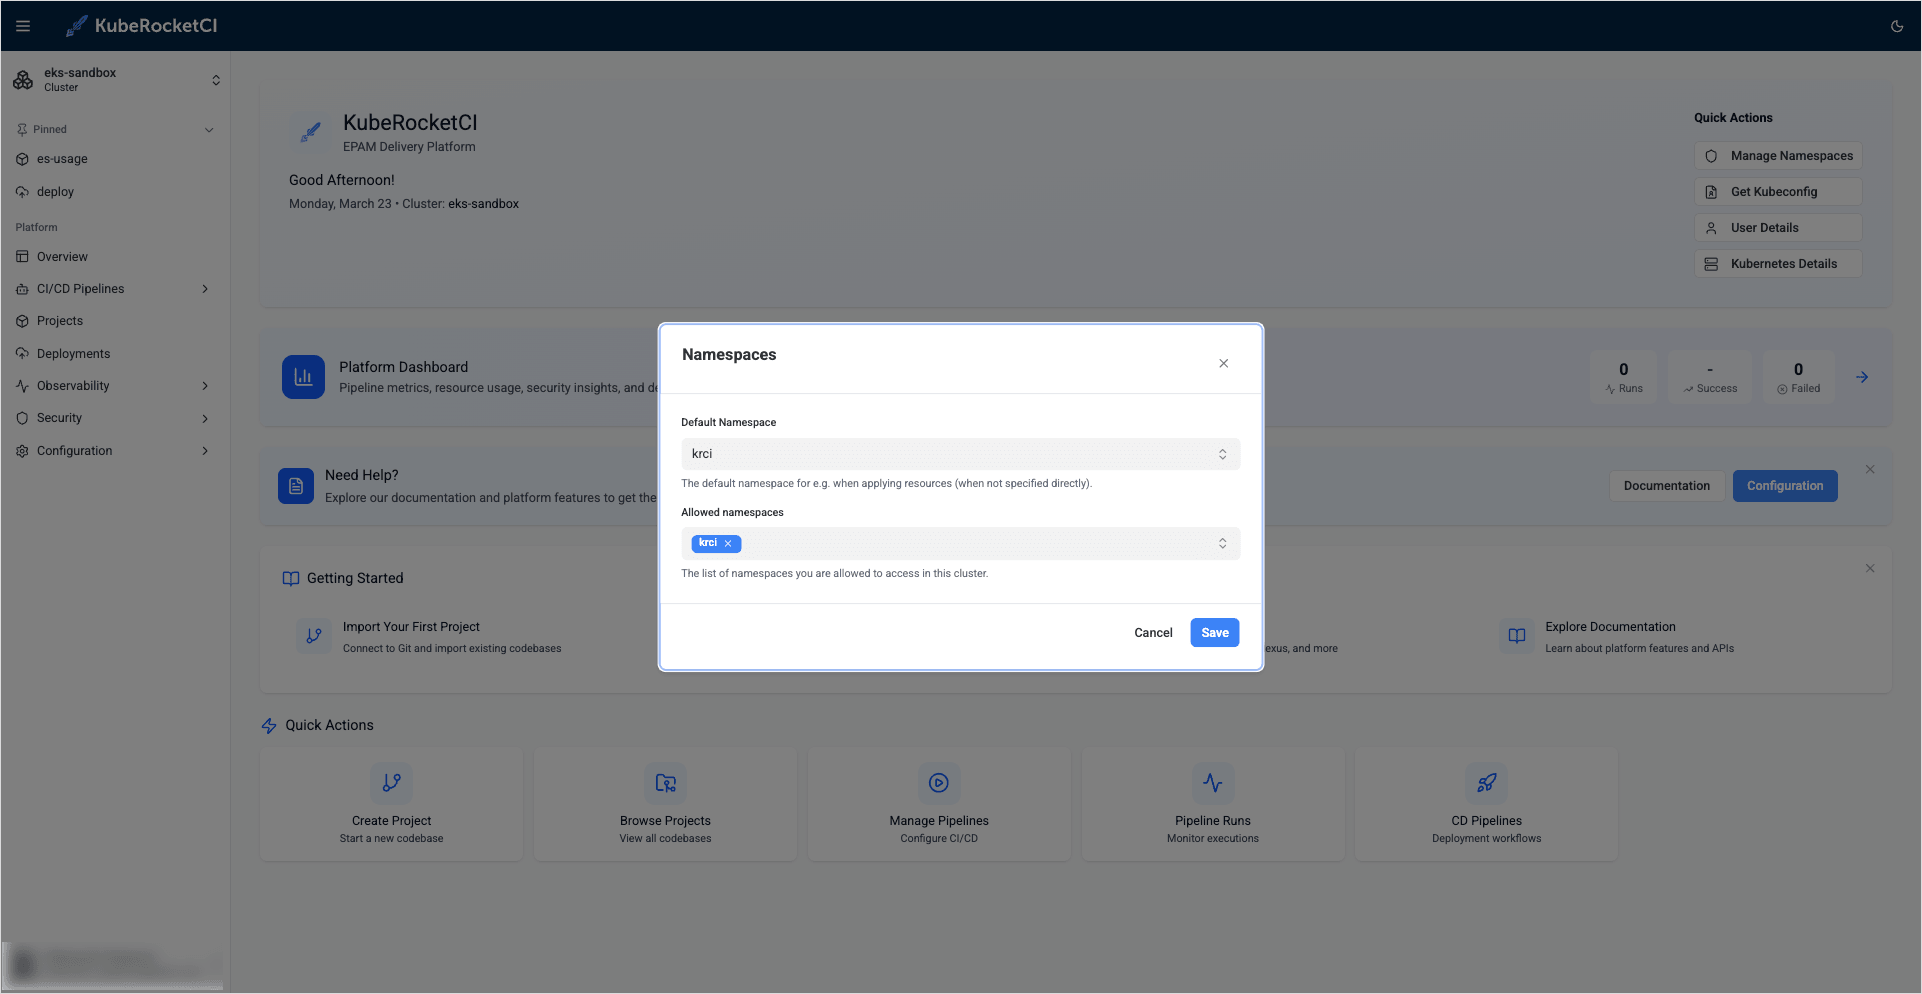
Ensure the
krcinamespace is specified in both default and allowed namespaces. If not, define them manually:- Default namespace:
krci - Allowed namespaces:
krci
 note
Remember to press Enter to add the allowed namespace to the list.
- Default namespace:
After completing these steps, you will gain access to KubeRocketCI components through the KubeRocketCI portal. You can now proceed with the integration steps, starting with the SonarQube integration.